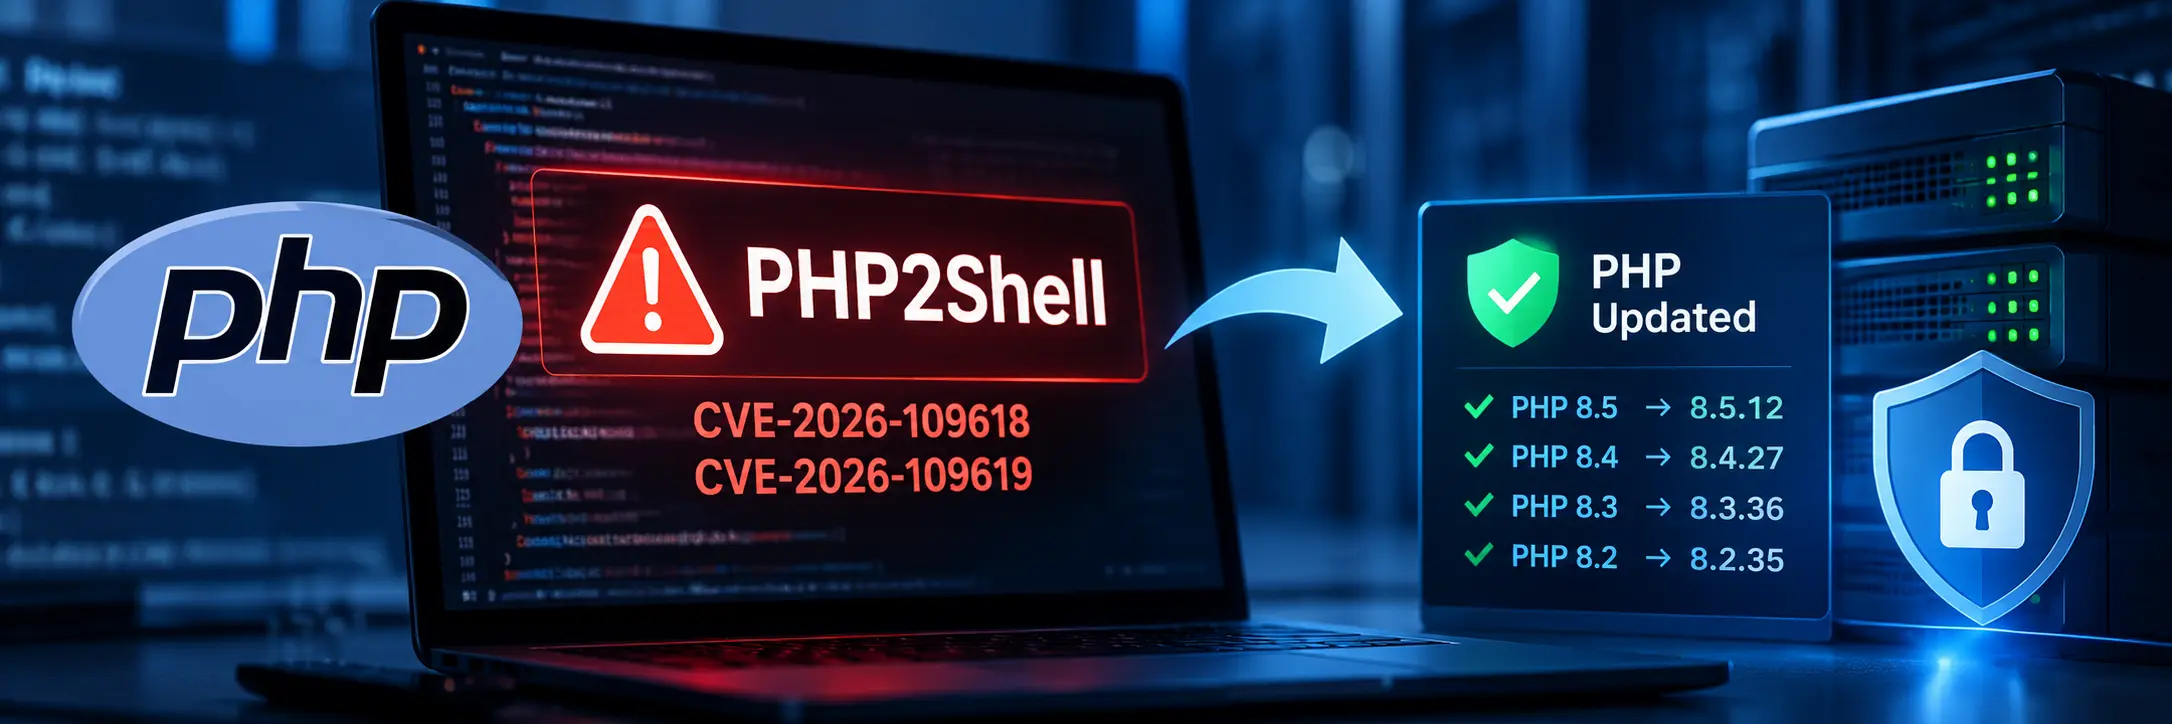
PHP security alert: On 21 October 2026, the PHP team released emergency security updates for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively known as PHP2Shell. These flaws can allow unauthenticated attackers to execute code on vulnerable servers.
The priority: identify affected PHP runtimes and install the appropriate security updates immediately.
What Are the PHP2Shell Vulnerabilities?
PHP2Shell refers to two critical vulnerabilities in PHP’s core runtime. Both are rated 9.2 under CVSS v4.0 and may allow remote code execution without authentication.
- CVE-2026-109618: Improper handling of out-of-memory errors can corrupt PHP’s internal request state.
- CVE-2026-109619: Stale references to previously freed request data can cause memory corruption.
These are PHP engine vulnerabilities, not ordinary application-level coding flaws. Applications using vulnerable PHP runtimes may be exposed even when their own code follows secure coding practices.
Which PHP Versions Are Affected?
The following releases address both vulnerabilities:
| PHP Branch | Fixed Version |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
Earlier versions in these branches are affected. PHP 8.1 and older branches are also affected but are end-of-life; move to a supported branch rather than relying on an unsupported runtime.
How to Fix PHP2Shell Quickly
1. Check Your PHP Version
Run the following command on the server:
php -vThis checks the CLI runtime. It may differ from the PHP version used by your website, PHP-FPM pool, container, or hosting panel. Verify each deployed runtime separately.
2. Upgrade to a Patched Release
Install the fixed version appropriate for your PHP branch using your operating system’s package manager, official PHP packages, hosting provider, or container image.
For example, on a Debian or Ubuntu server using distribution-managed PHP packages:
sudo apt update
sudo apt install --only-upgrade php8.3
Replace php8.3 with the relevant package and branch. Confirm that your configured repository actually supplies a patched build; distribution packages may use backported fixes and different version numbering.
For Docker-based deployments, update the PHP base image to a patched release, rebuild the image, and redeploy it.
3. Restart PHP and Web Services
After updating, restart the relevant PHP and web server processes so they load the patched runtime.
For example, on a system using PHP-FPM and Nginx:
sudo systemctl restart php8.3-fpm
sudo systemctl reload nginx
Adjust service names to match your installation. Apache with mod_php, other web servers, containers, and managed hosting environments require their corresponding restart or redeployment procedures.
4. Verify the Patch
Run:
php -vThen verify the PHP version serving actual web requests, not just the CLI version. Check application health, error logs, and service status after restarting.
Important: If you cannot patch immediately, restrict exposure or temporarily take the affected service offline where feasible. Web application firewalls and other temporary controls may reduce risk, but they are not a complete substitute for updating PHP.
Quick PHP2Shell Remediation Checklist
- Inventory all servers, containers, PHP-FPM pools, and hosted applications.
- Identify vulnerable PHP runtimes, including those behind control panels.
- Upgrade to a patched release or a vendor-confirmed fixed build.
- Restart or redeploy affected services.
- Verify the runtime serving web requests.
- Review system, web server, PHP, and security monitoring logs for suspicious activity.
- Investigate potential compromise if exposure occurred before patching.
- Plan migration away from end-of-life PHP branches.
Best Practices for PHP Runtime Security
- Apply PHP security updates as soon as they are released.
- Maintain an inventory of PHP versions across production and staging environments.
- Use supported PHP branches and monitor official security advisories.
- Automate dependency, container image, and runtime vulnerability scanning.
- Maintain tested backups and incident-response procedures.
- Treat patching and compromise investigation as separate tasks when a vulnerable server was internet-facing.
Conclusion
PHP2Shell highlights why runtime security updates must be treated as urgent engineering work. Developers and infrastructure teams should identify vulnerable PHP installations, deploy the available fixes, verify the running versions, and investigate signs of compromise where necessary.
FAQs
Can PHP2Shell be exploited without authentication?
Yes. Successful exploitation may allow an unauthenticated attacker to execute code on a vulnerable PHP server.
Is updating PHP enough to secure an already-exposed server?
Updating removes the known vulnerability when the correct fix is installed, but it does not remove malware or undo an earlier compromise. Review logs and investigate suspicious activity.
Can a Web Application Firewall fix PHP2Shell?
No. A WAF may help reduce exposure to known attack patterns, but it cannot provide a complete fix for these PHP engine vulnerabilities.
Does this affect WordPress and other PHP applications?
Potentially, yes. The risk comes from the underlying PHP runtime, so WordPress, Drupal, Joomla, and custom PHP applications may be affected when hosted on vulnerable versions.